Services
FISMA Assessment & Authorization
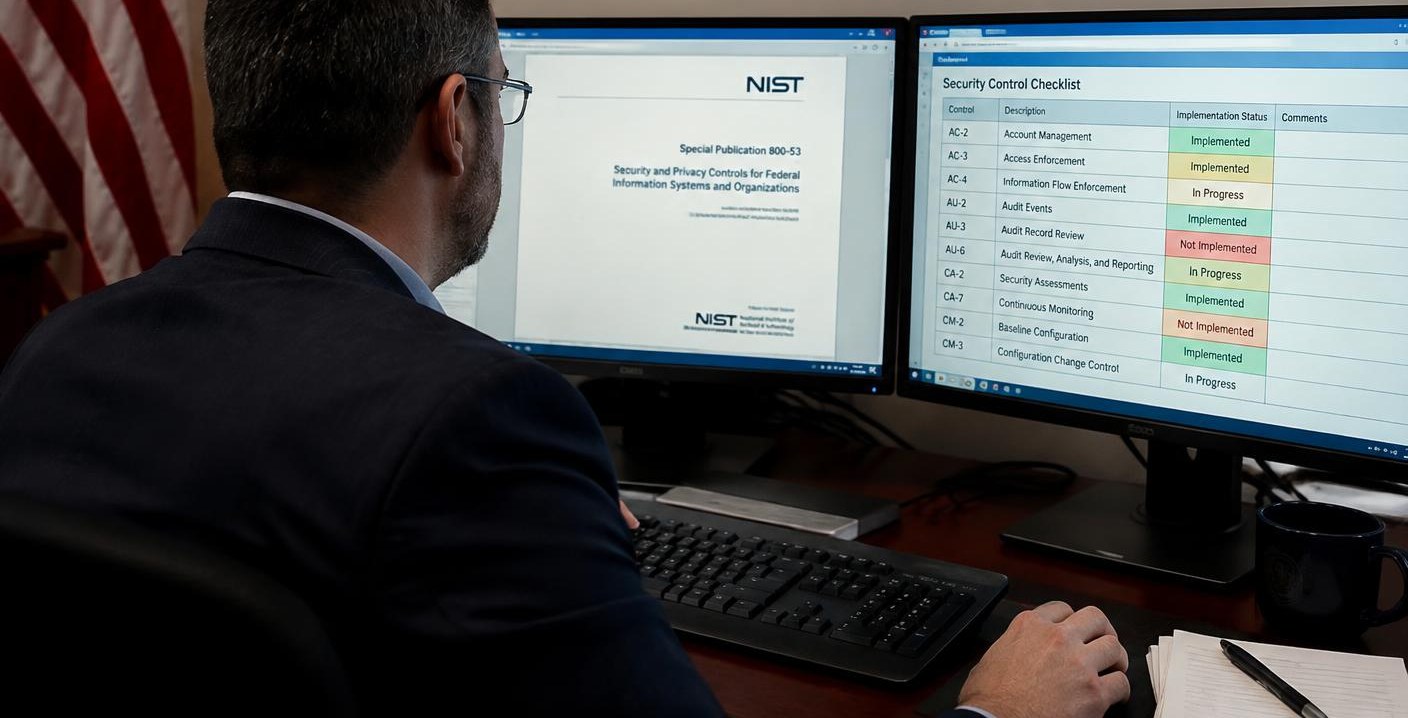
Federal systems must meet rigorous security requirements before and after they operate. ACSG supports agencies and their partners across the Risk Management Framework lifecycle, including System Security Plan development, risk assessments, control assessments, and authorization support. The authorization decision itself rests with the agency; ACSG helps you prepare a complete and defensible package.
What we provide
Complete Risk Management Framework Lifecycle
Support from categorization and control selection through assessment, authorization, and monitoring.
Security Control Implementation
Practical guidance for putting required controls in place and documenting them accurately.
Policy & Procedure Development
Clear, usable policies and procedures aligned to your system and agency requirements.
Security Control Assessments
Assessment of controls, supported by vulnerability assessment and penetration testing activities as scoped.
ISO/ISSO Support
Experienced support for information system owner and information system security officer responsibilities.
The value of the engagement
- System Security Plans that reflect the real system
- Risk assessments that inform decisions
- An organized authorization package for agency review
- Ongoing security support after authorization
Talk with an experienced cybersecurity advisor.
A focused, two-hour consultation tailored to your organization's cybersecurity goals and needs.